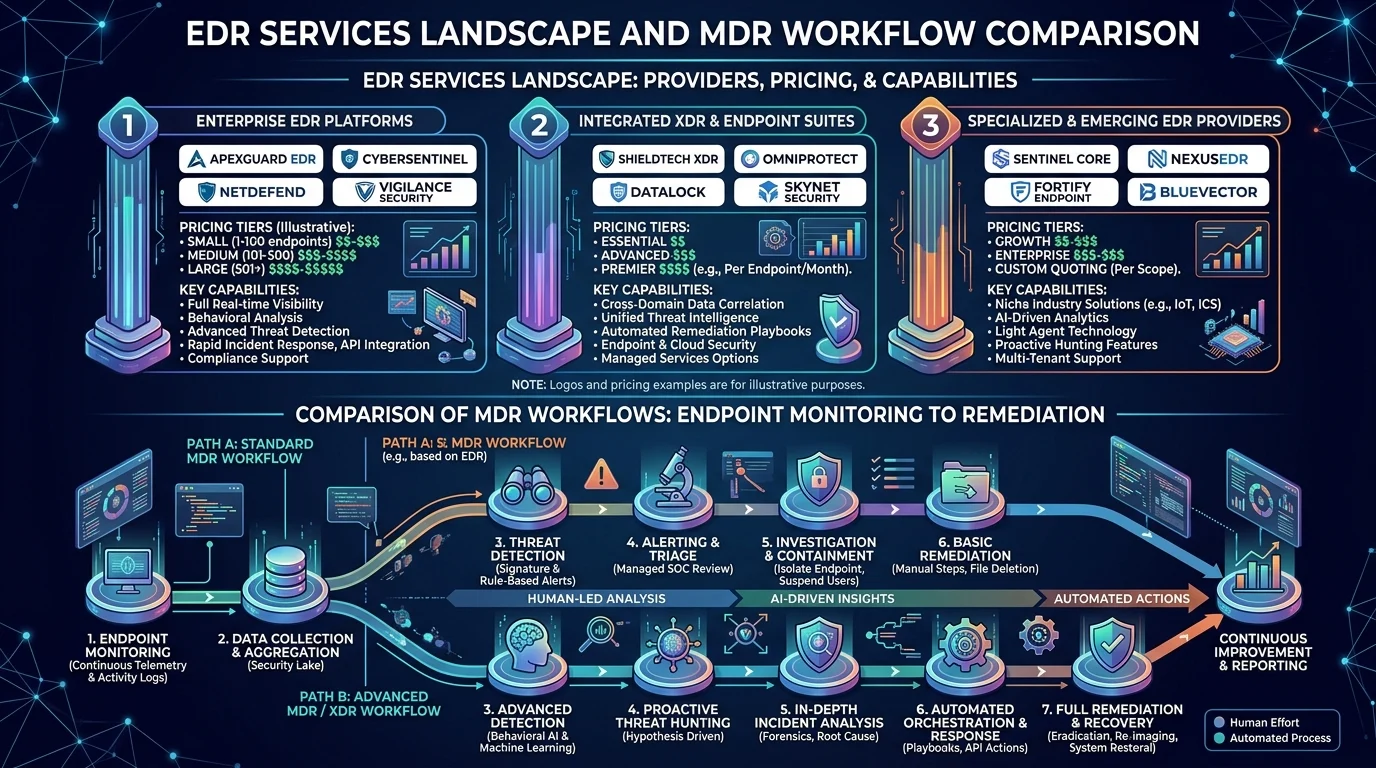
Quick Ans: Endpoint Detection and Response (EDR) services are managed cybersecurity offerings that provide 24/7 monitoring, threat detection, investigation, and response for endpoint devices. Key providers include BlueVoyant MDR, eSentire, Secureworks Taegis, Mandiant Managed Defense, and Red Canary. Pricing ranges from approximately $118 to $167 per user annually for Trellix MDR, with most enterprise solutions requiring minimum license commitments of 250 endpoints. The global EDR market is projected to reach $8.17 billion in 2026, growing at 27.3% CAGR.
Your security team is overwhelmed. Alerts flood in at all hours. Analysts are burned out. And somewhere in that noise, a real threat is hiding. This is the reality for countless organizations trying to defend their endpoints without the staff or expertise to do it alone.
Endpoint Detection and Response services solve this problem. These are managed offerings that combine EDR technology with human expertise, providing 24/7 monitoring, threat hunting, and incident response without requiring you to build and staff your own security operations center. Whether you call it MDR (Managed Detection and Response), Managed EDR, or co-managed SOC, the goal is the same: extend your security team’s reach with expert eyes that never sleep.
The market reflects this demand. The global EDR market is projected to reach $8.17 billion in 2026, growing at a remarkable 27.3% CAGR . Cloud-delivered agents controlled 68.12% of installations in 2025 and are growing at 24.93% CAGR . Organizations are realizing that buying technology isn’t enough. They need the people and processes that make it work. Let’s explore the EDR services landscape.
What Are Endpoint Detection and Response Services?
1. Managed Cybersecurity Offerings
EDR services are managed offerings that provide continuous monitoring and response for endpoint devices .
2. 24/7 Security Operations
Most services include round-the-clock monitoring by expert security teams .
3. Threat Detection and Investigation
Services identify, investigate, and help exterminate sophisticated cyberattacks .
4. Incident Response Capabilities
Providers help organizations respond to and recover from security incidents .
5. Threat Hunting Expertise
Services include proactive hunting for threats that automated tools might miss .
6. Technology Plus Human Expertise
EDR services combine endpoint detection technology with skilled security analysts .
7. Available Through Multiple Channels
Services are delivered by MSSPs, MDR vendors, and directly by platform providers .
8. Scalable for Different Organization Sizes
Offerings exist for small businesses, mid-market, and enterprise organizations .
9. Cloud-Delivered or On-Premises
Deployment options include cloud-delivered SaaS and on-premises or air-gapped solutions .
10. Integrated with Existing Security Stacks
Services integrate with SIEM, SOAR, identity, and other security platforms .
11. Compliance Support
EDR services help organizations meet regulatory requirements like NIS2 and HIPAA .
12. Strategic Control, Not Just a Tool
Industry leaders should treat EDR as a strategic control rather than a standalone tool .
Key EDR Service Providers
1. BlueVoyant MDR
Combines Microsoft Defender XDR with elite 24×7 security operations to identify, investigate, and exterminate advanced attacks .
2. eSentire Managed Detection and Response
Trusted MDR providing 24/7 threat investigations and response through Microsoft Defender XDR suite .
3. Secureworks Taegis ManagedXDR
24×7 managed detection and response service with threat hunting and incident response capabilities .
4. Mandiant Managed Defense
MDR service powered by dedicated frontline incident response experts protecting against motivated adversaries .
5. Red Canary MDR for Microsoft
24×7 managed detection, investigation, and response for threats in Microsoft environments .
6. Accenture Managed Extended Detection & Response
Fully managed service that proactively detects and mitigates advanced cyberattacks across IT and OT environments .
7. Dell Technologies Managed Security Services
Global service business with distributed Security Operations Center available 24/7 for security monitoring and management .
8. DXC Managed Endpoint Threat Detection and Response
Enables organizations to successfully detect and respond to threats, powered by Microsoft Defender for Endpoint and DXC experts .
9. Sophos MDR
Ranked #1 Overall in G2 Spring 2026 Reports for Managed Detection and Response .
10. Acronis MDR by Acronis TRU
Global MDR service for MSPs with round-the-clock threat monitoring and incident response, remediating critical incidents in as little as 15 minutes .
11. Trellix Managed Detection & Response
MDR service requiring minimum 250 EDR licenses, priced at $118.99 per user for 1-year subscription .
12. SonicSentry MXDR
Managed solution for MSPs built to protect clients across the entire attack surface with 24/7 SOC and NOC .
How EDR Services Work
1. Continuous Endpoint Monitoring
Services continuously monitor endpoints for evidence of threats and suspicious activities .
2. Data Collection and Analysis
Endpoint data is collected and analyzed using advanced analytics and machine learning .
3. Threat Detection
Services identify known and unknown threats using behavioral analysis and threat intelligence .
4. Alert Triage
Security analysts triage alerts to distinguish routine updates from critical threats .
5. Investigation
Experts investigate suspicious activities to determine scope and impact .
6. Threat Hunting
Proactive search for threats that automated tools might miss .
7. Response Actions
Services perform response actions like isolating endpoints, terminating processes, and quarantining files .
8. Incident Remediation
Experts help organizations recover from security incidents and restore operations .
9. Reporting and Communication
Clear alerts and reports keep organizations informed about security posture .
10. Integration with Security Stack
Services integrate with existing SIEM, SOAR, and identity platforms .
11. Compliance Support
Services help organizations meet regulatory requirements and demonstrate due diligence .
12. Continuous Improvement
After-action reviews and threat intelligence feeds improve future detection and response .
Pricing and Licensing
1. Trellix MDR Pricing
$123.35 list price, $118.99 discounted, per user for 1-year subscription with support .
2. Trellix Endpoint Security Suite + MDR
$174.25 list price, $167.57 discounted, per user for 1-year subscription .
3. Minimum License Requirements
Trellix requires at least 250 licenses of EDR (new or active subscriptions) .
4. SentinelOne Vigilance MDR
Adds cost per endpoint annually depending on service level and deployment size .
5. Arctic Wolf Multi-Year Discounts
2-year commitments achieve 10-15% lower annual pricing; 3-year commitments unlock 15-25% lower annual pricing .
6. Arctic Wolf Payment Terms
Annual prepayment typically includes 3-7% additional discount compared to quarterly or monthly payment .
7. CrowdStrike Falcon Complete
Fully managed MDR priced separately, with buyers negotiating per-endpoint pricing based on service-level requirements .
8. Hidden Costs to Consider
Professional services, extended data retention, premium support, and training add to total cost .
9. Volume Discounts
Buyers deploying 500+ endpoints often achieve lower per-endpoint pricing .
10. Competitive Leverage
Demonstrating credible competitive evaluation often achieves favorable pricing .
11. Multi-Year Savings
Buyers combining volume commitments, multi-year terms, and competitive leverage achieve strongest negotiated outcomes .
12. Renewal Pricing
5-15% price increases are common at renewal if not actively negotiated .
Key Capabilities to Evaluate
1. Detection Methodology
Look for multiple engines working together: signature-based, machine learning, and behavioral analysis .
2. Response Autonomy
Evaluate whether response is analyst-in-the-loop or autonomous, based on your risk tolerance .
3. Threat Hunting Depth
Assess the provider’s proactive hunting capabilities and adversary attribution depth .
4. Integration Ecosystem
Check compatibility with your existing SIEM, SOAR, identity, and cloud security platforms .
5. MITRE ATT&CK Mapping
Providers mapping detections to MITRE ATT&CK close visibility gaps and improve coverage .
6. Operational Metrics
Evaluate mean time to detect, mean time to contain, alert fidelity, and endpoint coverage .
7. Platform Portability
Consider skill portability if using Microsoft KQL versus Falcon-specific languages .
8. Public Sector Posture
For regulated industries, check FedRAMP, IL5, CMMC 2.0, and other certifications .
9. macOS and Linux Coverage
For heterogeneous environments, verify feature parity across operating systems .
10. MDR Service Scope
Clarify what’s included: 24/7 monitoring, response actions, threat hunting, and reporting .
11. Cyber Insurance Benefits
Some providers offer cyber warranty and discounted insurance with best-practice controls .
12. Onboarding Time
Estimated time to onboard varies from 3-5 days to 14-21 days depending on solution .
Choosing the Right EDR Service
1. Assess Your Internal Capabilities
If you lack 24/7 SOC coverage, MDR services fill that gap .
2. Define Your Threat Model
Prioritize providers matching your risk profile, whether minimizing dwell time or meeting compliance .
3. Consider Your Existing Stack
Microsoft-anchored organizations may benefit from Defender XDR integration .
4. Evaluate Total Cost of Ownership
Factor in base subscription, add-ons, professional services, and renewal pricing .
5. Check Minimum Commitments
Some providers require 250+ licenses, which may not suit smaller organizations .
6. Review G2 and Peer Ratings
Sophos MDR ranked #1 Overall in G2 Spring 2026 Reports .
7. Request Proof of Concept
Run parallel evaluations to test detection and response in your environment .
8. Negotiate Multi-Year Terms
Longer commitments unlock significant discounts but reduce future flexibility .
9. Start Renewal Negotiations Early
Begin 90-120 days before expiration to maximize leverage .
10. Leverage Competitive Alternatives
Demonstrating credible evaluation of alternatives achieves better pricing .
11. Clarify Hidden Costs
Extended retention, premium support, and training can add to total cost .
12. Plan for Integration
Improve endpoint coverage across servers, laptops, mobile, and cloud workloads .
Frequently Asked Questions
What are Endpoint Detection and Response services?
EDR services are managed cybersecurity offerings that provide 24/7 monitoring, threat detection, investigation, and response for endpoint devices .
How much do EDR services cost?
Trellix MDR starts at $118.99 per user annually. Most enterprise solutions require minimum 250 licenses. Multi-year commitments unlock 10-25% discounts .
What is the difference between EDR and MDR?
EDR is the technology. MDR is the managed service that combines EDR technology with human expertise and 24/7 monitoring .
What is the EDR market size?
The global EDR market is projected to reach $8.17 billion in 2026, growing at 27.3% CAGR .
Who are the top EDR service providers?
BlueVoyant, eSentire, Secureworks, Mandiant, Red Canary, Accenture, Dell, DXC, Sophos, and Trellix .
What is Sophos MDR?
Sophos MDR ranked #1 Overall in G2 Spring 2026 Reports for Managed Detection and Response .
Do I need EDR services if I have antivirus?
Yes. EDR catches advanced threats that bypass traditional antivirus, including fileless attacks and stolen credentials .
What is the minimum license for Trellix MDR?
Trellix requires at least 250 licenses of EDR (new or active subscriptions) .
How long does onboarding take?
Onboarding varies from 3-5 days to 14-21 days depending on the solution .
What discounts are available for multi-year contracts?
Arctic Wolf offers 10-15% lower annual pricing for 2-year commitments and 15-25% for 3-year commitments .
What is the difference between cloud-delivered and on-premises EDR?
Cloud-delivered controls 68.12% of installations and grows at 24.93% CAGR. On-premises retains 31.88% share for defense and regulated industries .
How does EDR integrate with SIEM?
EDR telemetry feeds into SIEM platforms for comprehensive security operations and correlation .
What is threat hunting?
Proactive search for threats that automated tools might miss, performed by expert analysts .
Conclusion
Endpoint Detection and Response services have become essential for organizations that need enterprise-grade security without building their own 24/7 SOC. The market’s explosive growth, projected to reach $8.17 billion in 2026, reflects the reality that buying technology isn’t enough. You need the people, processes, and expertise to make it work .
From BlueVoyant and eSentire to Sophos and Trellix, providers offer a range of options for different budgets and requirements. Pricing varies from $118 per user annually to custom enterprise agreements, with multi-year commitments unlocking significant savings. The key is matching your threat model, existing stack, and internal capabilities to the right service.
Whether you’re a small business needing basic MDR or a regulated enterprise requiring FedRAMP-authorized solutions, EDR services provide the expert eyes and rapid response that modern threats demand. Evaluate your options, negotiate strategically, and remember that the right partner can mean the difference between a contained incident and a catastrophic breach.
Discover More:
- Auto Response Email Templates: Complete Guide for 2026
- Michelle Obama Response: Complete Guide to Her Most Powerful Replies

1 thought on “Endpoint Detection and Response Services: Complete Guide for 2026”