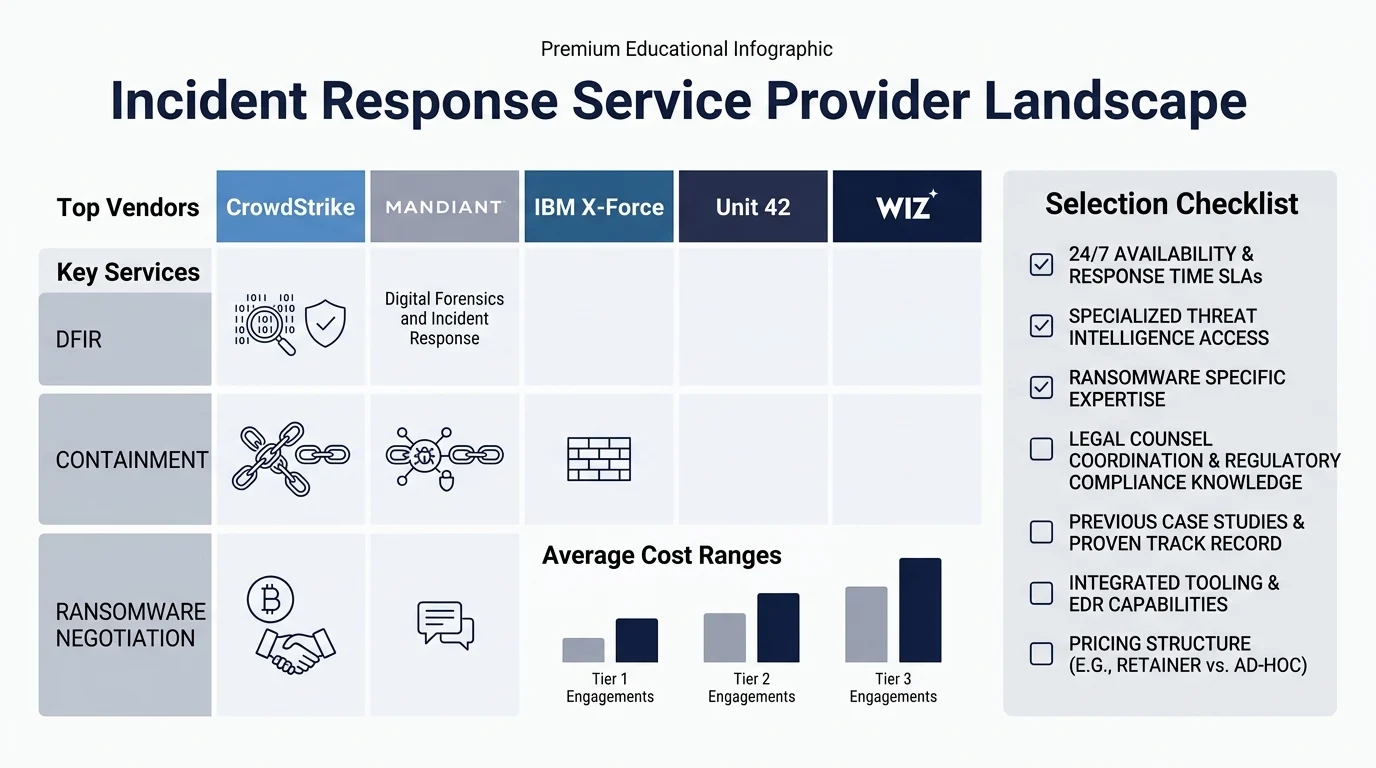
Quick Ans: An incident response service provider is a specialized cybersecurity firm that helps organizations detect, contain, investigate, and recover from cyberattacks. Key providers include CrowdStrike, Mandiant (Google Cloud), IBM X-Force, Palo Alto Networks Unit 42, and Wiz. Services typically include digital forensics, threat containment, root cause analysis, ransomware negotiation, and post-incident remediation planning. Costs range from $25-$45 per user monthly for software platforms to $5,000+ per incident for consulting services. Selection criteria include 24/7 availability, forensic depth, multi-environment capabilities, and regulatory compliance expertise.
When a cyberattack hits, every minute counts. The average data breach cost reached $4.45 million globally, and companies that respond quickly save approximately $1 million per breach compared to those that delay . That’s where an incident response service provider becomes your lifeline.
An incident response service provider is a specialized cybersecurity firm that helps organizations detect, contain, investigate, and recover from active security incidents. These providers combine digital forensics, threat intelligence, and expert-led containment to minimize damage and restore operations . Unlike general IT support, IR providers bring battle-tested expertise in ransomware takedowns, advanced persistent threats, insider attacks, and zero-day exploits.
The market is evolving rapidly. IDC observes that leading providers are deploying agentic AI architectures where AI agents autonomously conduct investigation, evidence collection, and response orchestration, with human analysts validating outcomes rather than performing tasks from scratch . This shift is particularly valuable for midmarket organizations that lack internal security head count .
Choosing the right provider can mean the difference between a contained incident and a catastrophic breach. Let’s explore what these providers offer and how to select the right partner.
What Is an Incident Response Service Provider?
1. A Specialized Cybersecurity Firm
Incident response service providers are dedicated firms that help organizations manage and recover from cyberattacks .
2. Focused on Active Incident Management
These providers specialize in detecting, containing, investigating, and remediating active security incidents .
3. Combines Forensics and Response
Services typically include digital forensics and incident response (DFIR), threat containment, root cause analysis, and remediation planning .
4. Offers 24/7 Availability
Reputable providers offer around-the-clock coverage with guaranteed response times .
5. Provides Expert-Led Containment
The best providers bring battle-tested defenders with real-world experience in ransomware, APTs, and insider threats .
6. Delivers Threat Intelligence Integration
Leading providers leverage real-time threat intelligence to understand attacker tactics, techniques, and procedures .
7. Supports Multi-Environment Forensics
Modern providers perform forensic analysis across networks, endpoints, SaaS, and cloud workloads .
8. Scales Communication for Stakeholders
Providers deliver executive-ready summaries, technical debriefs, and regulatory-ready documentation .
9. Operates as Retainer or Reactive Service
Organizations can choose between retainer models with guaranteed SLAs or reactive hourly services .
10. Integrates with Existing Security Tools
Providers work with your current SIEM, EDR, and other security investments .
11. Offers Proactive Preparedness Services
Many providers include readiness assessments, tabletop exercises, and compromise assessments .
12. Maintains Certified Forensic Expertise
Relevant credentials include GCIH, GCFA, GREM, EnCE, CFCE, and CISSP .
13. Provides Legal Defensibility
Providers with law enforcement or intelligence backgrounds add evidentiary rigor for litigation .
14. Addresses Regulatory Requirements
Services cover HIPAA, PCI-DSS, CMMC, SEC disclosure rules, and other frameworks .
15. Delivers Post-Incident Learning
Providers support after-action reviews and improvements to prevent future incidents .
Top Incident Response Service Providers for 2026
1. CrowdStrike Incident Response
Built around endpoint detection and response capabilities, supported by global threat intelligence and analyst teams .
2. Mandiant (Google Cloud)
Intelligence-led incident response with focus on advanced threats and complex investigations, now integrating with Google Cloud .
3. IBM X-Force
Global incident response with enterprise-grade integration across hybrid environments, combining human expertise with Watson for Cyber Security AI .
4. Palo Alto Networks Unit 42
Specializes in ransomware response and cloud security investigations, leveraging Palo Alto’s broad security portfolio .
5. Wiz Incident Response
Combines agentless cloud visibility with dedicated security expertise for fast investigation across cloud infrastructure .
6. Arctic Wolf
AI-powered security operations and incident response, recognized as a leader in IDC MarketScape for MDR midmarket .
7. Verizon Managed Security Services
Vendor-neutral approach with global SOCs, real-time threat monitoring, and incident analytics .
8. Getronics
Combines 24/7 SOC monitoring with enterprise log management, CSIRT, and incident response retainer support .
9. NetWitness
Offers incident response management with accelerated SLAs, deep threat expertise, and multi-environment forensics .
10. Check Point Incident Response
Structured services to address and mitigate security incidents efficiently, with worldwide technical support .
11. Prudential Associates
Medium enterprise focus pairing SOC-level detection with in-house digital forensics and legal defensibility .
12. Tencent Cloud CIRS
China-focused IR service with 1-hour workday response, 4-hour non-workday response, and self-developed automation tools .
13. KnowBe4 PhishER
Incident response software platform for phishing threat prioritization and containment, leader in G2 Grid Report .
14. Incident.io
Incident response software with on-call scheduling, Slack-native workflows, and self-serve setup .
15. PagerDuty
Incident response platform with on-call management and AIOps capabilities .
Key Services Offered by Incident Response Providers
1. Digital Forensics and Incident Response (DFIR)
Systematic investigation of security incidents to determine scope, impact, and root cause .
2. Threat Containment
Rapid isolation of affected systems to prevent lateral movement and further damage .
3. Root Cause Analysis
Determining how the attacker gained access and what vulnerabilities were exploited .
4. Malware Analysis
Reverse engineering malicious code to understand capabilities and indicators of compromise .
5. Ransomware Negotiation
Specialized experts who handle ransom demands and negotiate with attackers .
6. Evidence Preservation
Collecting and preserving forensic evidence for legal and regulatory purposes .
7. Timeline Reconstruction
Building a complete chronology of attacker activity using forensic artifacts .
8. Remediation Planning
Developing and executing plans to remove attacker persistence and restore systems .
9. Post-Incident Monitoring
Watching for signs of re-entry or related attacks after initial containment .
10. Executive Briefings
Providing leadership with clear, non-technical summaries of incident status and impact .
11. Regulatory Reporting Support
Assisting with breach notification requirements under HIPAA, PCI-DSS, SEC rules, and other frameworks .
12. Tabletop Exercises
Simulated incident scenarios to test organizational readiness .
13. Compromise Assessments
Proactive hunting for signs of undetected breaches .
14. Red Teaming
Adversarial simulations to identify security gaps before attackers do .
15. Crisis Management
Coordinating response across legal, communications, and executive teams .
How to Choose the Right Incident Response Provider
1. Evaluate 24/7 Availability and SLAs
A breach rarely waits for business hours. Look for guaranteed response times, not just “24/7” marketing .
2. Assess Forensic Depth
Certified specialists with GCIH, GCFA, GREM, and other credentials deliver materially more value .
3. Verify Multi-Environment Capabilities
Your provider should handle networks, endpoints, SaaS, cloud (AWS, Azure, GCP), and OT/IoT environments .
4. Check Intelligence Integration
Leading providers leverage real-time threat intelligence to understand attacker TTPs .
5. Review Communication Capabilities
Look for executive-ready summaries, technical debriefs, and regulatory-ready documentation .
6. Confirm Regulatory Expertise
If you’re in healthcare, finance, or defense, verify experience with HIPAA, PCI-DSS, CMMC, or SEC rules .
7. Understand Service Model Options
Decide between retainer (predictable cost, pre-established access) and reactive (no upfront cost, higher hourly rates) .
8. Ask About On-Site vs. Remote Response
On-site adds travel and surge-rate labor. Confirm what’s included for your environment type .
9. Evaluate AI and Automation Claims
Ask for specific AI outcome metrics rather than capability descriptions .
10. Request References
Speak with organizations of similar size and industry who have used the provider.
11. Review Legal Defensibility
If litigation is possible, prioritize providers with law enforcement or intelligence backgrounds .
12. Check Credential Verification
Verify certifications and experience of the actual responders, not just the sales team.
13. Understand Total Cost
Budget beyond the retainer or hourly rate: onboarding, environment assessment, and integration costs .
14. Test Communication During Sales Process
How responsive is the provider before you sign? That’s a preview of incident response .
15. Avoid Weak Providers
Steer clear of outsourced call centers, automation-only approaches, and providers who rush to mitigation without understanding root cause .
Incident Response Service Costs in 2026
1. Software Platform Pricing: $25-$45 per User Monthly
Industry range for complete incident response and on-call software solutions .
2. incident.io Pro with On-Call: $45 per User Monthly
Annual billing rate, includes unlimited on-call schedules and integrations .
3. PagerDuty Business: $41 per User Monthly
Base licensing, with AI and noise reduction add-ons priced separately .
4. Mandiant Hourly Rate: $519.99 per Hour
Listed price for Mandiant incident response service through CDW .
5. Tencent Cloud CIRS: 21,200 RMB per Incident
For 1-10 assets, with 1-hour workday response and 4-hour non-workday response .
6. AWS Incident Response: $5,000+ per Event
Entry threshold for AWS incident response services .
7. Reactive IR: High Per-Hour Rates During Crisis
No upfront cost but no guaranteed availability when you need it most .
8. Retainer IR: Predictable Cost with Proactive Services
Pre-established access, readiness assessments, and tabletop exercises included .
9. Hidden Costs: Setup and Integration
Legacy platforms can require weeks of engineering time, burning $4,000+ in internal costs .
10. On-Site Response Premium
Travel, logistics, and surge-rate labor add significant costs .
11. Regulated Industry Premium
Healthcare at $7.42M and financial services at $5.56M average breach cost versus $4.44M global average .
12. Retainer Value: Tabletop Exercises Reduce Dwell Time
One tabletop exercise can surface gaps that extend dwell time and drive up breach cost by more than the retainer fee .
13. AWS Pricing: Per Event, High Threshold
按事件计费,门槛高 .
14. Minimum Asset Requirements
Tencent CIRS: 1 asset minimum. Huawei: 5 assets minimum. AWS: high threshold per event .
15. ROI from MTTR Reduction
Unified tooling can reduce MTTR by up to 80% compared to legacy/manual processes .
Frequently Asked Questions
What is an incident response service provider?
It’s a specialized cybersecurity firm that helps organizations detect, contain, investigate, and recover from active security incidents .
What services do incident response providers offer?
Services include digital forensics, threat containment, root cause analysis, ransomware negotiation, evidence preservation, and post-incident remediation .
How much do incident response services cost?
Software platforms range from $25-$45 per user monthly. Consulting services start around $5,000 per incident or $519.99 per hour for premium providers .
What’s the difference between retainer and reactive IR?
Retainers provide predictable costs and guaranteed availability. Reactive services have no upfront cost but convert to high hourly rates during a crisis .
How quickly should an incident response provider respond?
CrowdStrike’s 1-10-60 rule sets the benchmark: detect in 1 minute, investigate in 10, contain in 60. Retainers with SLAs approaching this threshold price accordingly .
What credentials should IR specialists have?
Relevant credentials include GCIH, GCFA, GREM, EnCE, CFCE, and CISSP .
Can incident response providers handle cloud environments?
Yes. Leading providers perform forensic analysis across AWS, Azure, GCP, and Kubernetes .
What is agentic AI in incident response?
Agentic AI architectures allow AI agents to autonomously conduct investigation, evidence collection, and response orchestration, with human analysts validating outcomes .
How do I choose the right incident response provider?
Evaluate 24/7 availability, forensic depth, multi-environment capabilities, intelligence integration, communication, and regulatory expertise .
What are red flags when selecting an IR provider?
Avoid outsourced call centers, automation-only approaches, and providers who rush to mitigation without understanding root cause .
Do incident response providers help with regulatory reporting?
Yes. Providers assist with breach notification under HIPAA, PCI-DSS, CMMC, SEC rules, and other frameworks .
What is the average cost of a data breach?
The global average is $4.45 million. Healthcare averages $7.42M and financial services averages $5.56M .
Conclusion
An incident response service provider is your organization’s emergency room for cyberattacks. These specialized firms bring the forensic expertise, threat intelligence, and rapid containment capabilities that internal teams often lack. From digital forensics and ransomware negotiation to regulatory reporting and post-incident learning, the right provider transforms a chaotic breach into a managed response.
The market is evolving fast. IDC observes that agentic AI architectures are separating leading providers from those still using AI-augmented human models . Midmarket organizations stand to benefit most, as AI-driven efficiency gains directly translate into faster response and broader coverage .
When selecting a provider, prioritize 24/7 availability with guaranteed SLAs, deep forensic credentials, multi-environment capabilities, and regulatory expertise. Understand the total cost beyond hourly rates and retainers, including onboarding, environment assessment, and integration work . Avoid weak providers that rely on outsourced call centers or automation without human expertise .
Your incident response provider is a critical partner in your security strategy. Choose wisely, test regularly, and keep the relationship strong before you need it. When the next breach hits, you’ll be glad you did.
Discover More:
